On October 27, 2026, Optimizely published a security advisory regarding recently disclosed Node.js vulnerabilities affecting Node.js 22.x, 24.x, and 26.x release lines. Optimizely confirmed there is currently no evidence of exploitation across Optimizely products or customer environments.
For most SaaS customers, remediation is handled automatically by Optimizely. However, certain CMS, Commerce Connect, and Frontend Hosting customers may need to take action to ensure they receive the patched Node.js runtime.
Executive Summary
The first question many Optimizely CMS customers asked was:
“Does this affect my Optimizely CMS PaaS solution?”
According to guidance received from Optimizely Support, customers using CMS PaaS generally only need to take action if their solution proxies Node.js processes through their .NET application.
“Customer only needs to act if they proxy Node.js processes through their .NET application. They must deploy a code package with a new name or version number. The package can contain the same code that’s in production. This forces a container rebuild that picks up the patched Node.js.”
This clarification aligns with Optimizely’s published security advisory, which identifies customers proxying Node.js workloads and customers using Frontend Hosting as requiring action.
How to Determine Whether You Are Affected
Step 1: Check if Your Solution Uses Node.js
For many Optimizely CMS DXP solutions, the Node.js version is defined in:
src/[Client Repository]/dxpPlatformSettings.json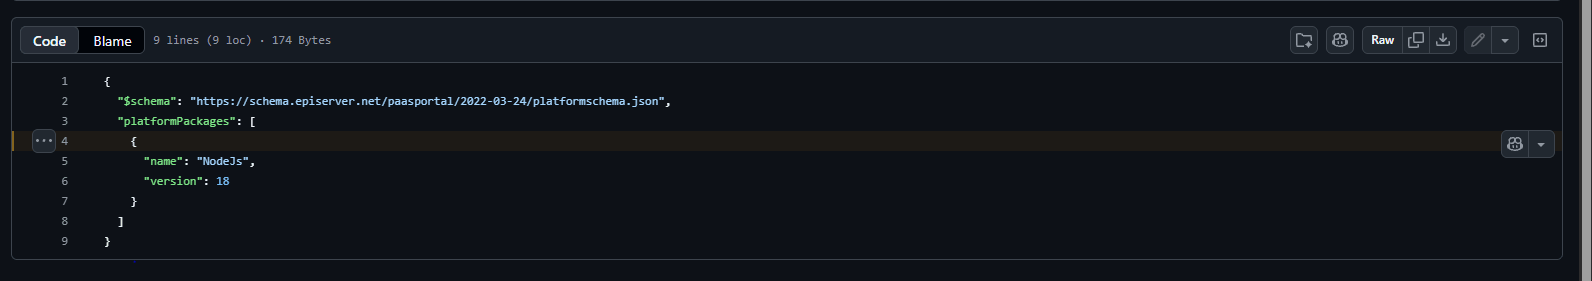
nodeVersion value indicates which major Node.js runtime version will be used when DXP builds your container image.Step 2: Identify the Version
| Node.js Version | Status |
|---|---|
| 18.x | End of Life – Upgrade Required |
| 20.x | End of Life – Upgrade Required |
| 22.x | Supported – Requires rebuild to receive patched runtime |
| 24.x | Supported – Requires rebuild to receive patched runtime |
| 26.x | Supported – Requires rebuild to receive patched runtime |
Step 3: Verify Whether Your Deployment Uses Node.js
You are most likely affected if your solution:
- Uses Optimizely Frontend Hosting
- Runs Next.js, React, Vue, Angular, or other Node-based applications
- Proxies Node.js processes from an ASP.NET application
- Uses Node.js during build or runtime execution on DXP
Optimizely identified these scenarios as requiring customer action.
The Fix for DXP Customers
The good news is that the fix typically does not require code changes.
Optimizely’s DXP build pipeline automatically retrieves the latest patched Node.js version for your configured major version whenever a new container image is built.
To receive the patched runtime:
-
Create a new deployment package.
-
Change the package name or version number.
-
Deploy the package through the standard DXP deployment process.
-
Allow DXP to rebuild the container image.
What About .NET Security Updates?
During discussions with Optimizely Support, customers were also directed to Microsoft’s out-of-band October 2026 .NET security updates.
If your solution includes .NET workloads, review the Microsoft guidance and evaluate whether your environment requires additional patching alongside the Node.js remediation effort.
Optimizely Support further advised:
“We do not have a specific recommendation regarding the timing of the upgrade. However, since this issue involves a security vulnerability, we recommend upgrading as soon as feasible. Ultimately, your organization will need to assess and accept the associated risks based on your own security requirements and policies.”
This is a sensible approach. While no active exploitation has been reported by Optimizely, security-related rebuilds and upgrades are typically best scheduled as part of the next available maintenance window while following your organization’s risk management process.
Hope this helps.
Happy Optimizing!


